- A vendor domain, and a TLS connection to it.
- A category in a proxy log.
- That someone opened an assistant.
- What was actually asked, and what came back.
- Whether an agent acted on the answer, or a person did.
- Which of those sessions touched something that matters.
- Whether a revoke you issued still holds at the point of use.
- See
Surface unsanctioned use
Discover the AI tools and GenAI sessions employees use that your security stack can't see — across the browser plane and the system plane.
- Comprehend
Read the session, not just the vendor
Knowing which assistant someone opened is inventory. The CognitionAI Engine reads what was actually exchanged inside it — what a person asked, what came back, and what agents said to each other — so ordinary use separates from the session putting scoped data somewhere it should not go.
- Neutralize
Governed, not blocked
Sanction a tool or revoke it and have the decision hold at the point of interaction, with enforcement scoped to autonomous activity — so the productivity that drove adoption survives the governance.
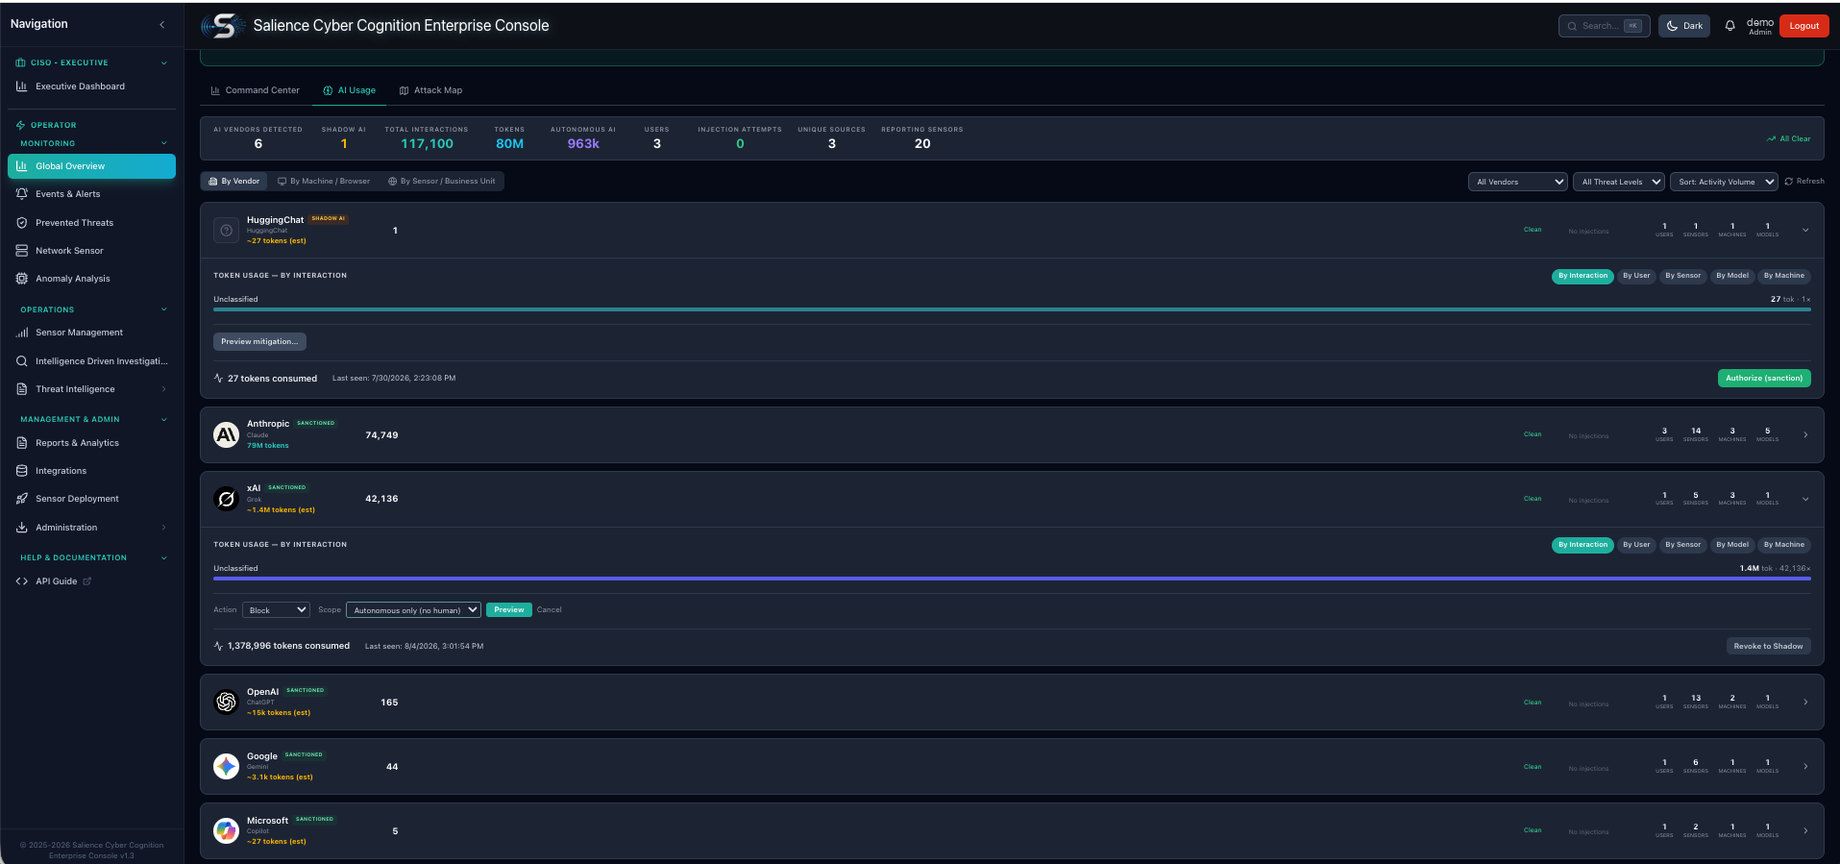
Shadow AI, Sanctioned or Blocked
Vendor-by-vendor usage with sanction and revoke — and enforcement scoped to autonomous activity, leaving human workflows untouched.
See the full product tour