See
Flow, process, parent, binary
Host to parent to process to destination, sized by volume — with connections that routed around the proxy surfaced rather than absent, because they never reached the log you were watching.
The data left. It did not go through your proxy, so it is not in the egress record you review, and the connection that carried it was opened by a process an AI session wrote days earlier. SalienceCyber.ai ties that flow back to the process, the process back to the session, and stops the connection at the host.
Host to parent to process to destination, sized by volume — with connections that routed around the proxy surfaced rather than absent, because they never reached the log you were watching.
Artifacts created in an AI session are recorded at birth, so a binary that executes days later is already bound to the interaction that produced it — provenance, not inference.
The connection neutralized at the system plane by a userspace host sensor — not a kernel agent — at the moment the process reaches for a destination it was never meant to have.
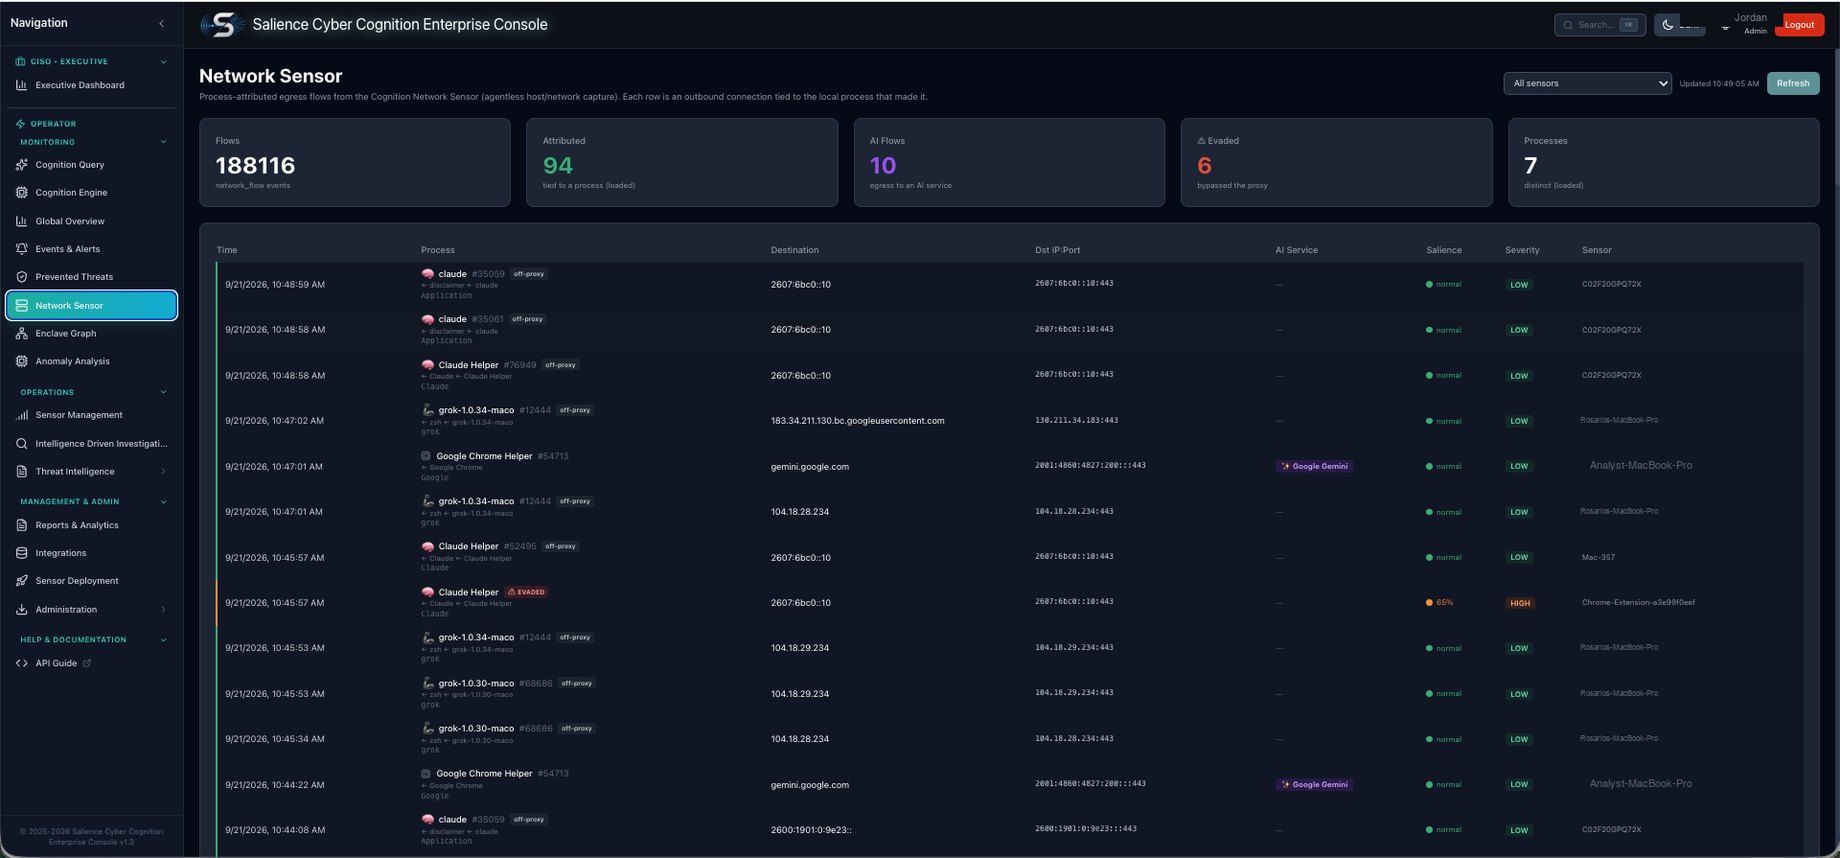
Every outbound connection tied to the local process that opened it — and the ones that bypassed the proxy counted out on their own.
See the full product tour