See
Catch it in the session
Direct and indirect prompt injection — including payloads hidden in a web page — surfaced at the browser plane as the interaction happens.
Direct and indirect prompt injection — including payloads hidden in a web page — surfaced at the browser plane as the interaction happens.
The CognitionAI Engine reads the intent inside the prompt, distinguishing a benign request from an injected instruction with no known signature.
Neutralize the injected interaction at the point of use — before it exfiltrates data or opens a connection — with no analyst in the loop.
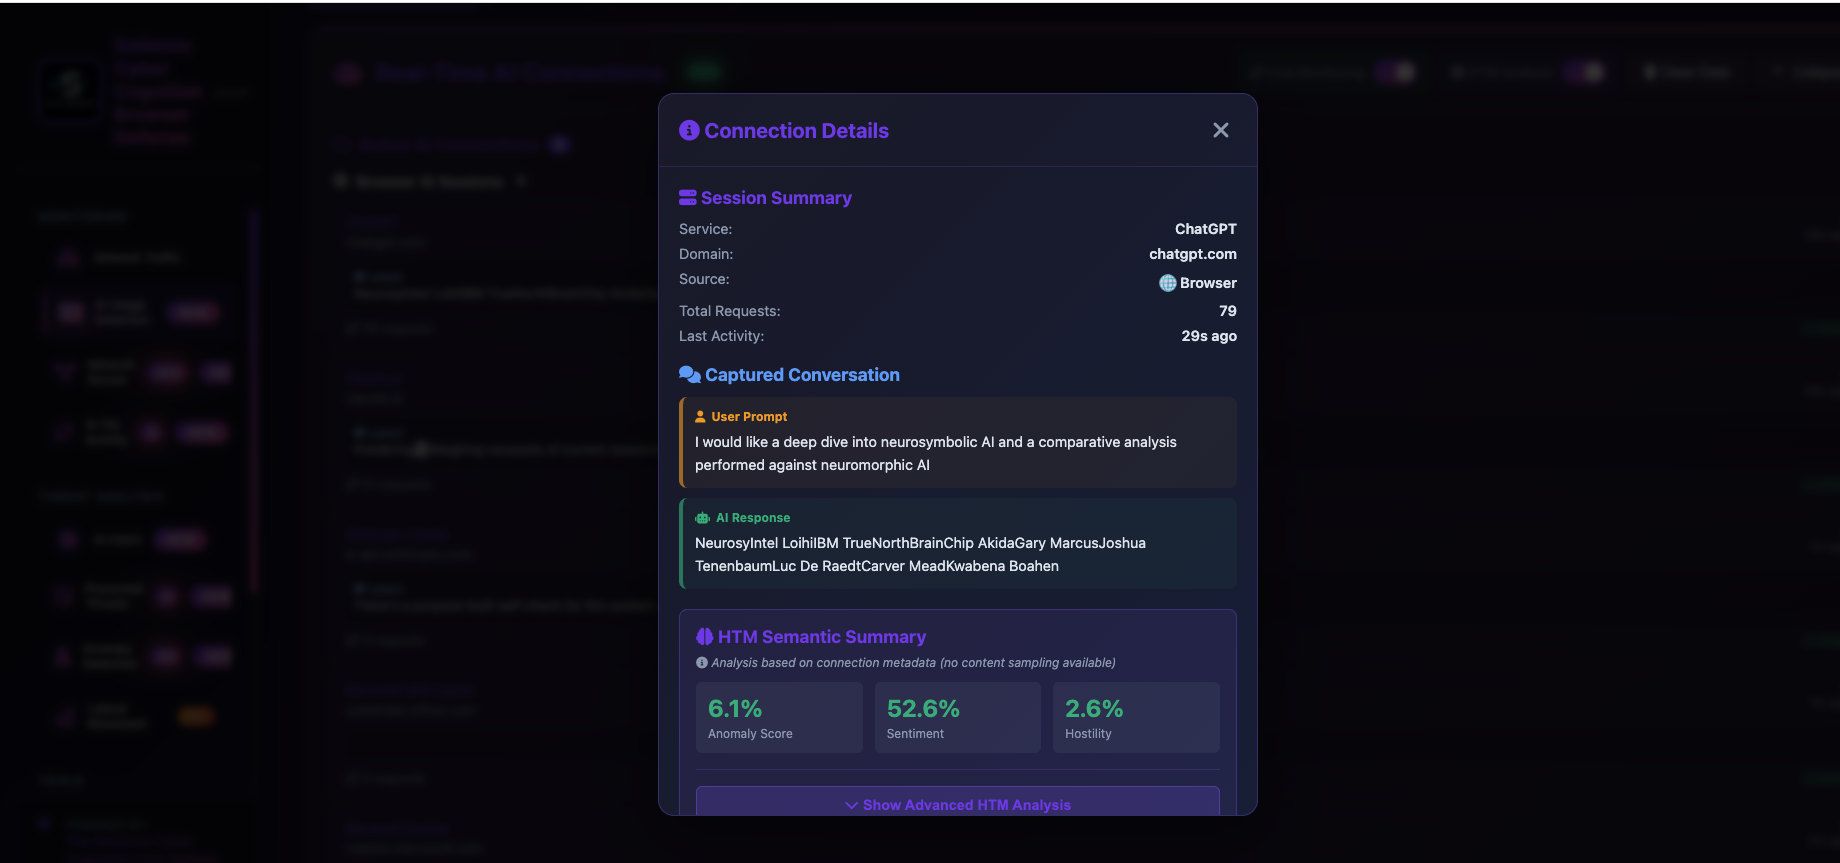
The captured exchange, scored for anomaly, sentiment, and hostility — read at the semantic layer rather than matched against a signature.
See the full product tour