The insider now has an assistant.
A departing engineer asks a chat assistant to summarise the customer list, then to reshape it as a spreadsheet. Every system they touched, they were authorised to touch. This is the AI-mediated slice of insider risk — the exchanges that happen inside an assistant session, where DLP and UEBA have nothing to read. SalienceCyber.ai reads what is actually being asked of the AI, and stops the request that crosses the line.
- An authorised user, on a sanctioned tool.
- A system they were entitled to touch.
- No rule tripped, because no rule was broken.
- That the summary request was staged collection.
- That the next prompt reshaped it for export.
- That the same person asked twice, three weeks apart.
- Intent — which is the only thing that separates the two.
- See
Every session, attributed
Every AI interaction across the browser plane and the system plane — sanctioned tools and shadow AI alike — tied to the session, the process, and the user that produced it.
- Comprehend
What is actually being asked
The CognitionAI Engine reads the intent inside the exchange, separating a routine summarisation request from staged collection of material someone is preparing to take.
- Neutralize
Before the answer comes back
The hostile interaction stopped at the point of use — no analyst in the loop, no alert queue to grade, and no dependency on the employee tripping a rule they already know about.
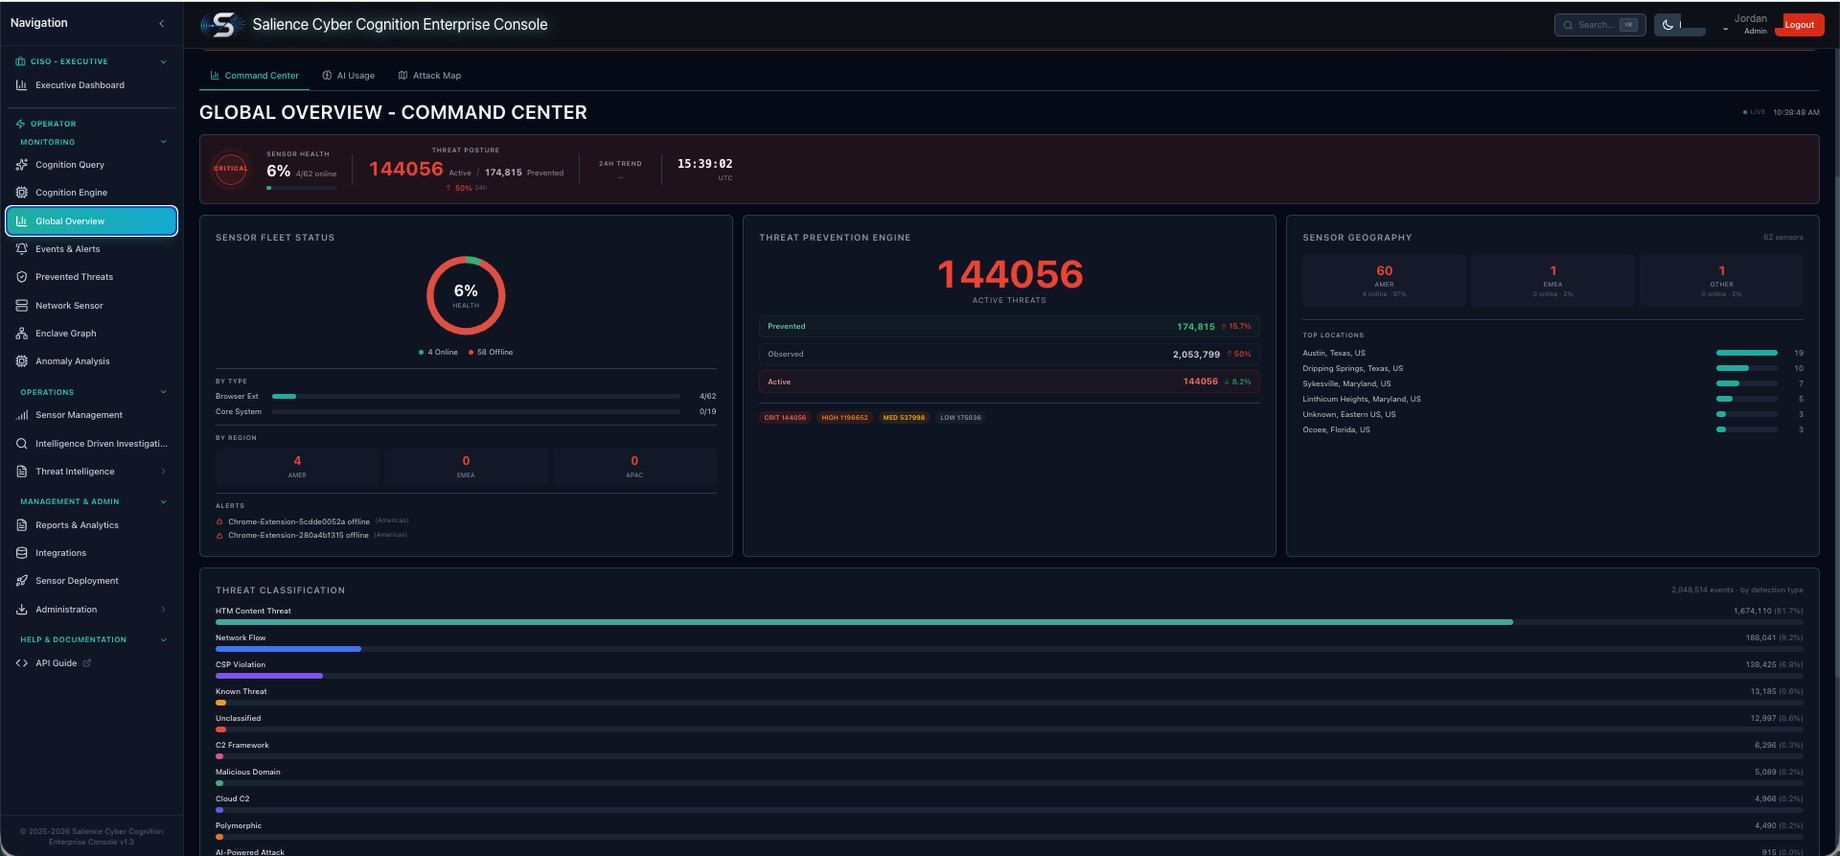
The Number on the Board
Fleet health, prevention posture, and where AI risk is concentrating — the same telemetry that stopped the interaction, in the language of the board.
See the full product tour