Where AI adoption opens a door, we close it at runtime.
Two ways to read this page. What changes for the business — cost, deployment, and what your team stops having to do — and the ten technical places AI adoption opens a door.
247 documented incidents735 cited sources118 confirmed intrusionsSearch the Threat Ledger →What it changes for the business.
Prevention is the product. One claim, seen four ways: cost does not move when AI adoption does.
- Cost0No token spendper-token charges, at any volumeSee the engine →
- EconomicsFlatA flat, predictable TCOcost curve as AI adoption scalesWhy Salience →
- DeploymentDay 1Fast time to deploymentfrom kickoff to full protectionSee the platform →
- Operations1Awareness and enforcementone product for both planesTour the console →
What it stops.
Three classes of AI-driven attack. Ten places they show up. One decision system that reads intent in every direction of exchange.
Familiar tradecraft executed at a speed and scale human defenders cannot match.
Prompt injection and agentic exploitation — attacks aimed at the AI systems your teams now depend on.
Novel, polymorphic payloads written by a model, carrying no prior signature to match.
Ten use cases, three families.
Grouped by what the attacker is actually doing — targeting your AI, using it as an author, or moving through it to reach your data.
Attacks that target your AI
The model, the agent, and the tool calls between them are now the asset under attack. These are the interactions no signature has ever seen, because the payload is language, not code.
Attacks your AI writes
When a model is the author, there is often no prior artifact to match — a payload novel on arrival, whether it compiles or simply persuades.
Data and access moving through AI
The assistant is the new egress path. It is authenticated, it is trusted, it is unlogged by the controls you already own — and it will summarise anything you give it.
See. Comprehend. Neutralize.
Ten use cases, one decision path. The CognitionAI Engine runs it on both planes — a userspace host sensor, not a kernel agent, paired with an AI-aware extension in the browser.
- 01
See
DiscoverVisualizeObserveFind the AI in use, render it legible, and watch it continuously — across the browser plane and the system plane, sanctioned or not.
- 02
Comprehend
Human → AIAI → HumanAI → AIRead the intent in every direction of exchange: what a person asks of AI, what AI returns to them, and what AI systems say to each other — agent to agent, tool call to tool call.
- 03
Neutralize
AI-EnhancedAI-NativeAI-GeneratedStop all three AI-driven threat classes before they execute: attacks sharpened by AI, attacks that target AI itself, and attacks authored by AI.
Not a slide deck. Unedited capture.
Four recordings of the platform working across both planes, each one standing behind the use cases named beside it.
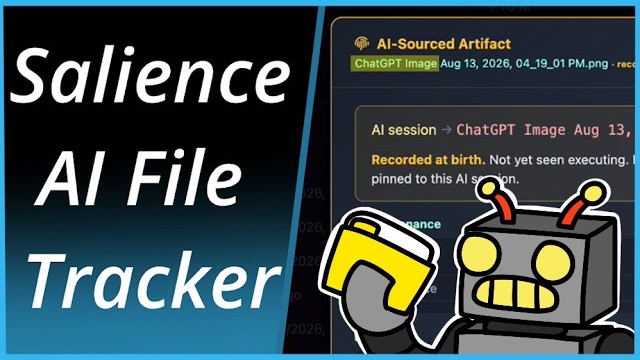 Discover every file moving to and from AIStands behind · Insider threat · Industrial espionage
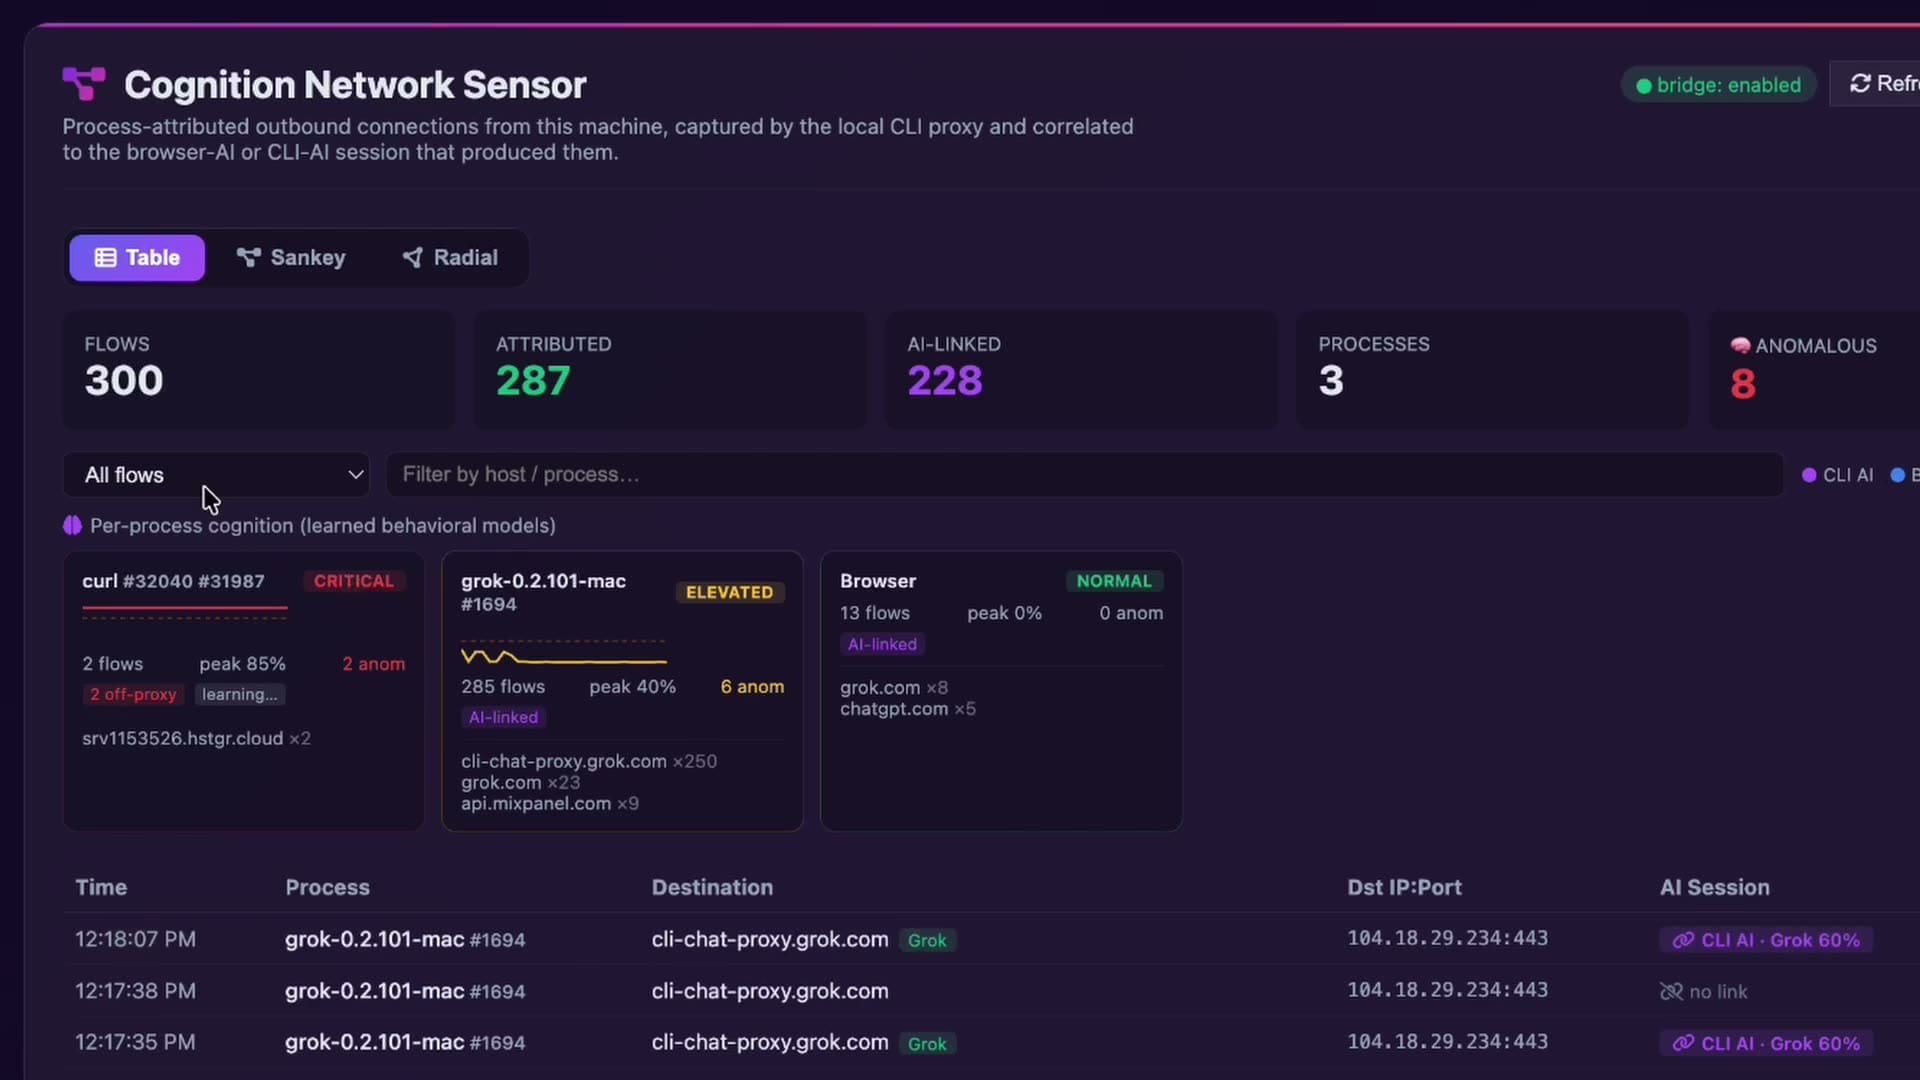 Track the risky files and processes AI createsStands behind · Covert exfiltration · AI-generated malware
 See every use of AI on a machineStands behind · Shadow AI · Model integrity & sovereignty
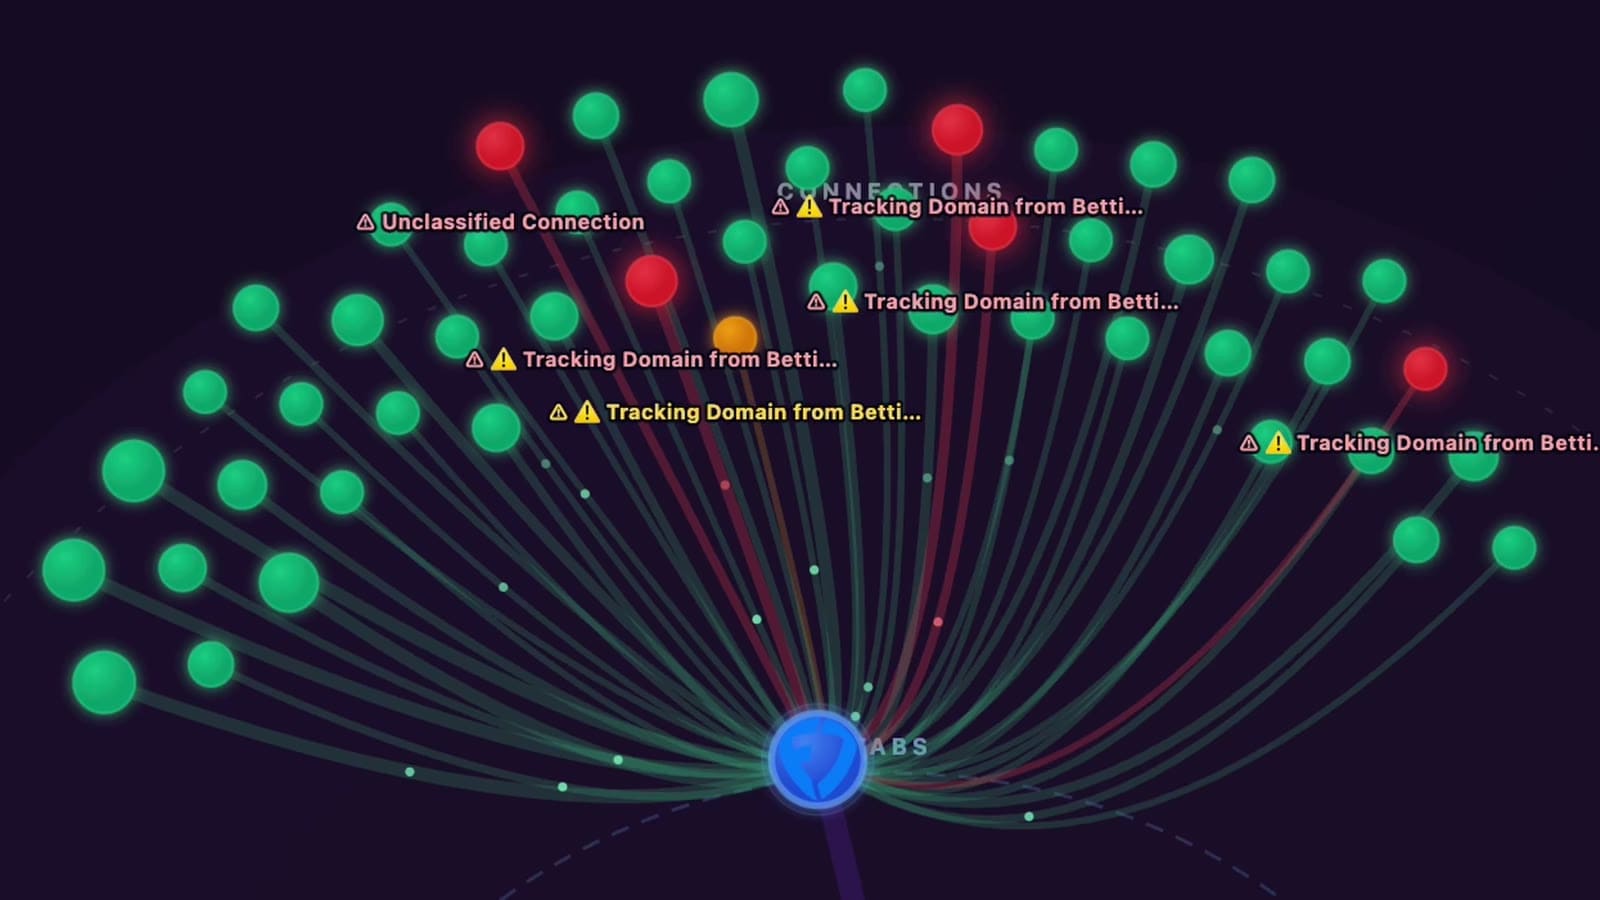 Real-time traffic analysisStands behind · Agentic exploitation · Covert exfiltration